Towards a strong European cybersecurity environment

A strong cybersecurity environment poses a key priority for Europe’s economy. As the use of digital solutions grows, the need to ensure that Europe’s networks and information systems are resilient against evolving cyberattacks is paramount. Our suggestions for an improved resilience of the EU’s cybersecurity focus on the scope of the proposal for a revised Directive on Security of Network and Information systems (NIS 2 Directive), the risk-based approach, proportional obligations, legislative overlap and conflicting requirements as well as offering insight on reporting obligations and thresholds. Read our response here.

News
3 Jul 2021
Digital
Towards a strong European cybersecurity environment

As the EU’s economy and society continue to embrace digital solutions in an accelerated fashion, the need to ensure that Europe’s networks and information systems are resilient against evolving cyberattacks has never been higher. A strong cybersecurity environment is thus a key pillar for both industry and government stakeholders alike. To achieve a more resilient cybersecurity, increased collaboration through public-private-partnerships, harmonization and global cooperation will be paramount going forward. The European Commission’s proposal for a revised Directive on Security of Network and Information systems (NIS 2 Directive) aims to address these issues and to increase cyber resilience across the EU.

To ensure the European Commission’s ambitions can become a reality and contribute to a safer and stronger cybersecurity environment, AmCham EU puts forward a number of recommendations to further enhance the legislative proposal. Our suggestions for an improved resilience of the EU’s cybersecurity focus on the scope of the NIS 2 Directive, the risk-based approach, proportional obligations, legislative overlap and conflicting requirements as well as offering insight on reporting obligations and thresholds. Furthermore, AmCham EU offers insights on how to ensure a more streamlined industry involvement as well as on certification, international standards, and encryption. Moreover, we highlight crucial angles of the discussion around vulnerability disclosures, supervision and enforcement, as well as remaining issues on the provisions focusing on top level domain registration data.

Related items

Position Paper
10 Nov 2026

Making web scraping rules work for AI

The European Data Protection Board’s draft guidelines on web scraping for generative AI are an opportunity to provide greater legal certainty and support Europe’s AI competitiveness. However, some proposed requirements risk creating disproportionate burdens for AI developers.

A pragmatic, risk-based approach is needed to ensure the rules reflect the technical realities of AI development. This includes proportionate transparency obligations, recognition of the need for diverse training datasets and greater alignment with the AI Act and Digital Omnibus. Clear, harmonised rules are essential to protect personal data while enabling innovation.

Read our consultation response to learn more about the recommendations.

Digital
Read more
Read more about Making web scraping rules work for AI
News
6 Nov 2026

Digital Economy Conference 2026: in review

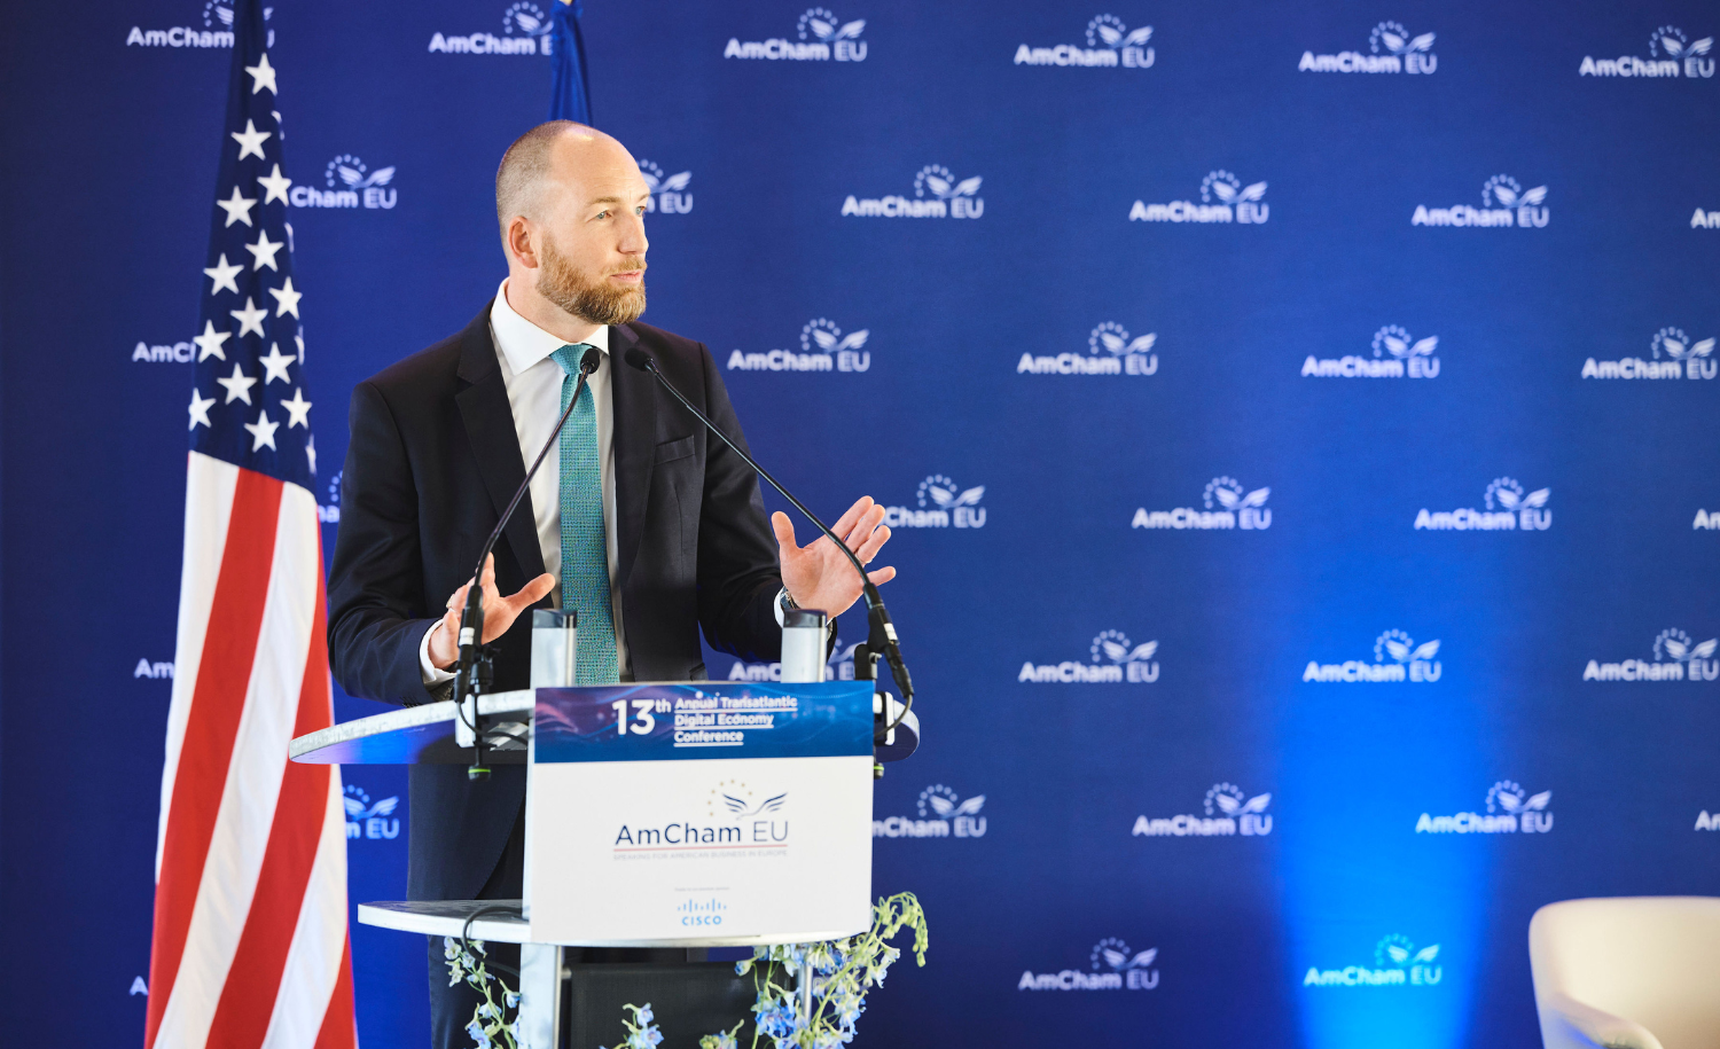
AmCham EU’s 13th Annual Transatlantic Digital Economy Conference took place on Thursday, 5 November, under the theme Cutting through complexity. The event brought together policymakers, regulators and industry leaders to discuss how clear, workable frameworks and closer EU-US cooperation can bring more coherence to the digital landscape and support economic growth.

Digital
Read more
Read more about Digital Economy Conference 2026: in review
Position Paper
7 Oct 2026

Making CADA’s sovereignty framework work for Europe

The success of the Cloud and AI Development Act (CADA) will depend on whether its sovereignty framework strengthens Europe’s resilience and competitiveness without restricting access to the technologies, providers and operating models needed to support the bloc’s digital transformation. As currently envisaged, several elements of CADA introduce origin-based restrictions that are not necessarily linked to genuine sovereignty, security or resilience risks. These measures could reduce competition, increase costs and slow cloud and AI adoption – ultimately working against CADA’s underlying objectives.

A sovereignty framework built on objective, risk-based criteria will better support Europe’s competitiveness, resilience and digital transformation than one based on origin, ownership or nationality.

Digital
Read more
Read more about Making CADA’s sovereignty framework work for Europe